Skip to content

ISO27001-certified incident management software for healthcare
AdobeStock_247860824

Healthcare organizations need software they can trust with sensitive information. When incident management involves patient, employee and organizational data, information security needs to be part of the solution from the start.

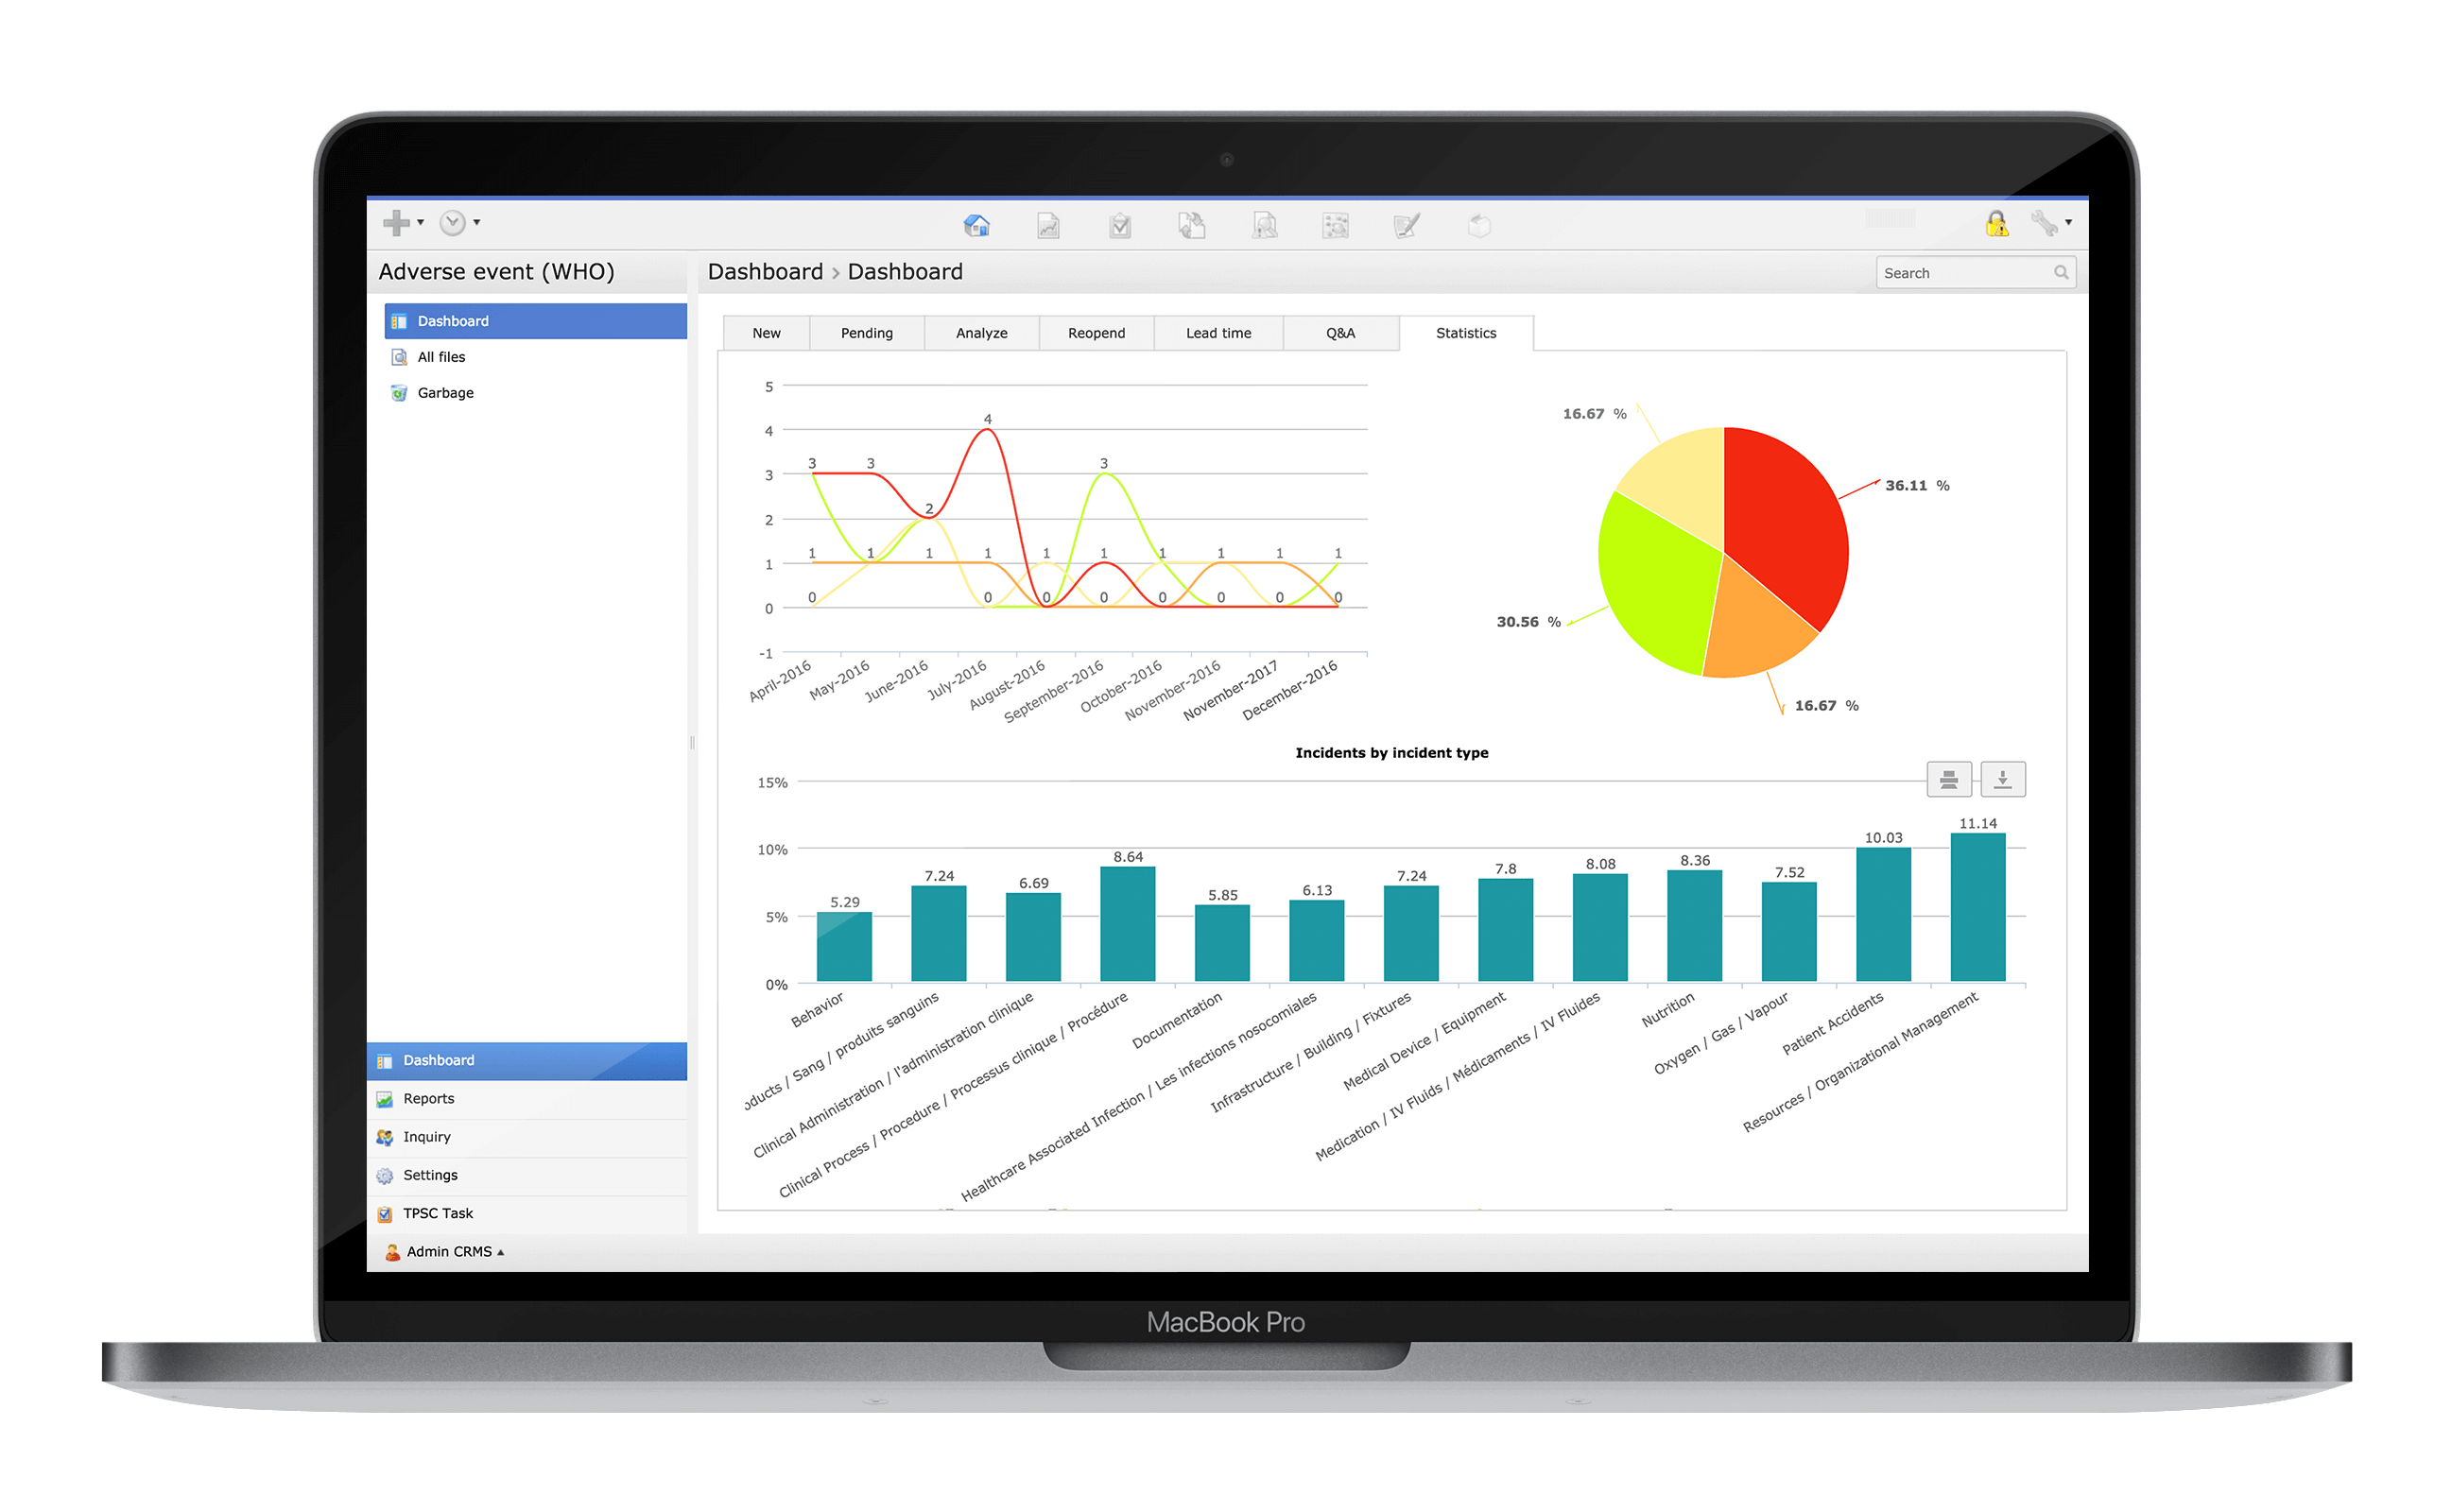
At The Patient Safety Company (TPSC), we are ISO/IEC 27001-certified, demonstrating our commitment to managing information security and risk systematically. TPSC Cloud™ provides a secure environment for managing incidents and patient safety data, while supporting healthcare organizations in learning from incidents and improving care.
What is ISO 27001 certification?

ISO/IEC 27001 is an internationally recognized standard for information security management systems (ISMS). It provides a framework for identifying security risks, implementing appropriate controls and continuously improving how information is protected. An organization that is ISO 27001-certified has been independently assessed against the requirements of the standard, providing assurance that information security is managed systematically across the organization.

Confidentiality, integrity and availability

ISO 27001 focuses on three fundamental aspects of information security: confidentiality, integrity and availability. Confidentiality means that information is accessible only to authorized people. Integrity ensures that information remains accurate and complete and is protected against unauthorized changes. Availability means that authorized users can access information when they need it.

For healthcare organizations, these principles are particularly important. Software used to manage incidents and patient safety data can contain sensitive information that needs to be protected throughout its lifecycle.

Ready to see how easy incident reporting can be for your team?

Schedule a free online demo or discuss your needs with a specialist.

  • Learn things like creating an incident reporting form
  • See how easily you can analyse incidents and quality-related data
contact.png?width=230&height=250&name=contact

What does it mean that TPSC is ISO 27001-certified?

Being ISO/IEC 27001-certified means that TPSC's information security management system has been assessed against the requirements of the international standard. For our customers, this provides independent assurance that security is embedded in the way we manage our organization, processes, systems and controls.

Our approach includes:

  • Structured information security and risk management
  • Defined policies, responsibilities and controls
  • Controlled access to information and systems
  • Ongoing assessment of security risks
  • Regular review and improvement of security measures
  • Independent assessment of our information security management system

ISO 27001 certification does not mean that every security risk can be eliminated. Instead, it demonstrates that risks are identified, assessed and managed through a consistent framework. Effective information security requires ongoing attention as technologies, threats and organizational needs evolve.

How does TPSC maintain ISO 27001 certification?

Achieving ISO 27001 certification is only the beginning. Maintaining it requires information security to remain an active part of our organization and day-to-day operations. At TPSC, we regularly assess risks, review our controls and identify opportunities for improvement. This helps us adapt to changing technologies, emerging threats and evolving customer requirements.

Regular audits and independent assessments also play an important role. They help verify that our information security management system continues to meet the requirements of ISO/IEC 27001 and remains effective over time.

The benefits of ISO 27001 certification

Choosing an ISO 27001-certified software provider like TPSC gives healthcare organizations additional assurance when evaluating how their data is handled. So, what does ISO 27001 certification mean in practice? Here are five key benefits for healthcare organizations.

1. Independently assessed information security

Certification provides external verification that an organization's information security management system meets the requirements of an internationally recognized standard. This gives healthcare organizations additional assurance beyond a software provider's own statements about its security practices.

2. A consistent approach to managing risk

Healthcare organizations face a range of information security risks. ISO 27001 provides a framework for addressing these through defined processes, responsibilities and controls across people, processes and technology.

3. Protection of sensitive information

Patient safety and incident management can involve sensitive information about patients, employees and healthcare processes. Protecting the confidentiality, integrity and availability of this information is therefore an essential consideration when choosing software.

4. Continuous improvement

Information security cannot stand still. Technologies, threats and organizational requirements change over time. ISO 27001 supports an ongoing cycle of reviewing risks, evaluating controls and improving security practices.

5. Greater confindence when choosing a software provider

Security is an important consideration when selecting a technology partner in healthcare. Working with an ISO 27001-certified provider can provide additional assurance when assessing how a supplier manages information security and associated risks.
Why ISO 27001 certification is important

Cloud-based healthcare software enables organizations to collect, manage and analyze information efficiently. At the same time, sensitive data needs to be protected throughout its lifecycle. In incident management, this can include information about patients, employees, incidents, investigations and improvement activities.

ISO 27001 provides a recognized framework for managing information security through policies, processes, controls and risk management. For healthcare organizations, this provides an important reference point when evaluating how software providers manage the security of their data.

At TPSC, information security is an integral part of how we develop and operate our software and organization. Our ISO/IEC 27001 certification provides independent assurance of this approach. We also recognize that information security requirements can differ between countries and healthcare systems. Alongside our ISO/IEC 27001 certification, we therefore work with relevant local and regional standards and certifications where applicable. This allows us to address the specific information-security requirements of different markets and healthcare environments.

Successfully certified to ISO/IEC 27001

Our ISO/IEC 27001 certification reflects our commitment to protecting information and continuously improving our approach to information security. For healthcare organizations, this means you can choose TPSC Cloud™ knowing that the information security management system behind the platform has been independently assessed against an internationally recognized standard.

ISO 27001 provides a recognized framework for managing information security through policies, processes, controls and risk management. For healthcare organizations, this provides an important reference point when evaluating how software providers manage the security of their data.

At TPSC, information security is an integral part of how we develop and operate our software and organization. Our ISO/IEC 27001 certification provides independent assurance of this approach. We also recognize that information security requirements can differ between countries and healthcare systems. Alongside our ISO/IEC 27001 certification, we therefore work with relevant local and regional standards and certifications where applicable. This allows us to address the specific information-security requirements of different markets and healthcare environments.

Our valued customers include